
A backup becomes valuable at the exact moment the primary system can no longer be trusted. Until then, it is only a stored promise. Enterprise teams often measure job completion, storage consumption, and retention coverage, yet leave the harder question unanswered: can the business restore the right application, in the right order, within its approved recovery window?
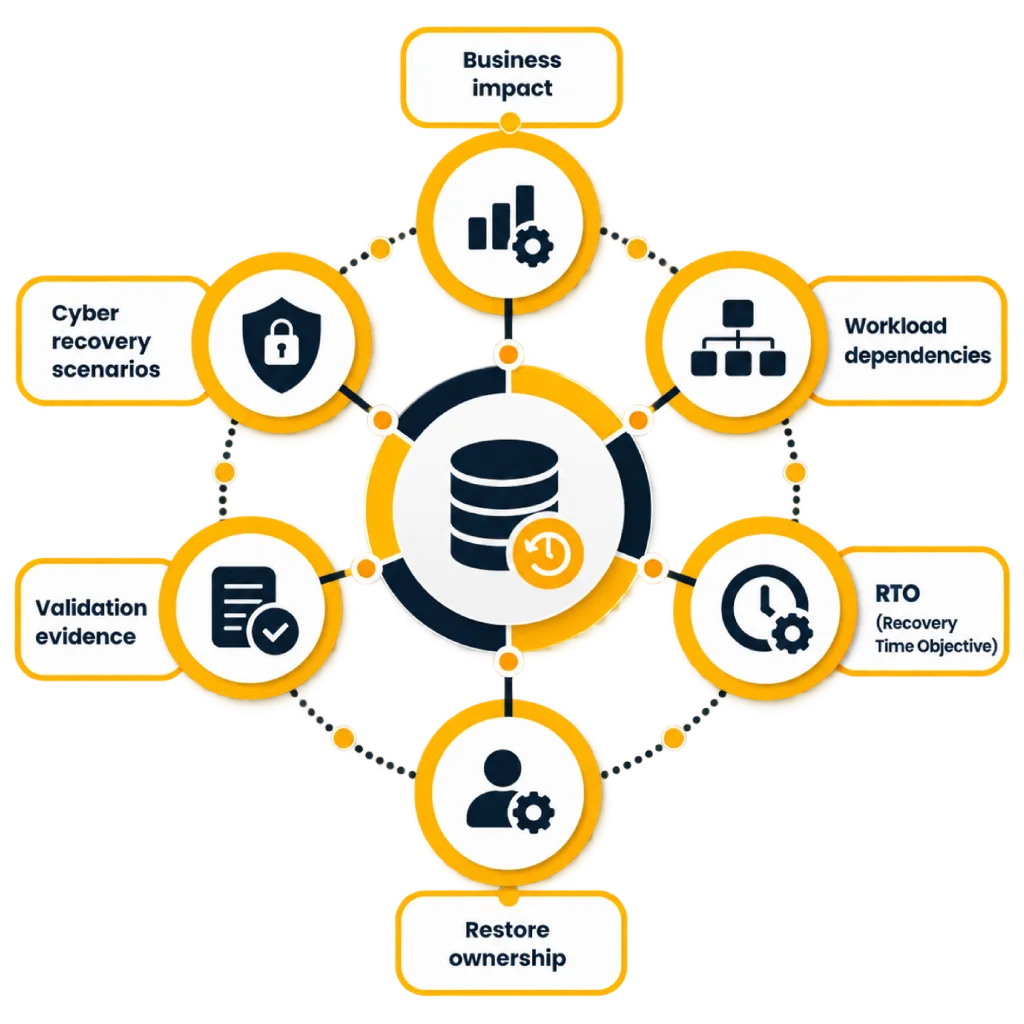
A credible AWS backup strategy starts with recovery evidence, where aws cloud consulting services help define backup architecture, recovery objectives, cross-account protection, and compliance controls. It connects business impact, workload dependencies, recovery point objectives, recovery time objectives, and restoration ownership. The goal is not to collect more copies. It is to create recoverable states that remain usable after deletion, corruption, ransomware, account compromise, or a regional disruption.
Why Enterprise Backup Design Starts with Recovery Intent
Enterprise estates rarely have one recovery requirement. A payment database may tolerate minutes of data loss. A document archive may tolerate a day. Development environments may need no retained copy when infrastructure and test data can be recreated.
Treating these workloads alike raises cost without improving protection. Effective AWS data protection classifies applications before assigning technology. Each application should have:
- A business owner who approves recovery objectives
- A technical owner who maintains restore procedures
- A defined recovery sequence for data, identity, networking, and application services
- A retention basis tied to operational, legal, or contractual needs
- A scheduled test that proves the recovery path
This classification becomes the control plane for AWS backup policies enterprise teams can apply across accounts. Tags can connect resources to policy tiers, while AWS Organizations backup policies can distribute requirements centrally. Governance should follow workload purpose rather than whichever service happens to store the data.
Classification also prevents policy drift. When teams create schedules independently, similar applications can receive different retention periods without a defensible reason. A shared recovery catalogue gives security, infrastructure, application, and compliance teams one record of what is protected, why it is protected, and who approves exceptions.
Backup and Disaster Recovery Solve Different Failures
Backup preserves restorable data. Disaster recovery restores an operating service. The distinction matters because a valid database snapshot cannot rebuild missing IAM roles, DNS records, certificates, network routes, application configuration, or deployment artifacts.
| Discipline | Core question | Typical measure | Failure if ignored |
| Backup | Can the required data be restored? | Recovery point age | Data is missing or corrupted |
| Disaster recovery | Can the service resume? | RTO and RPO | Data exists, but the application remains unavailable |
| Business continuity | Can the business keep operating? | Process tolerance | Technology recovers before operations do |
An AWS disaster recovery backup plan should therefore include infrastructure definitions, dependency maps, restoration steps, validation queries, and traffic cutover procedures, similar to the discipline used in a resilient multi-account AWS architecture. AWS guidance places backup and restore among several DR approaches, generally suited to workloads that can accept longer recovery windows. Faster objectives may require pilot light, warm standby, or multi-site designs.
Which AWS Services Protect Enterprise Data?
AWS Backup provides centralized policy, scheduling, lifecycle management, monitoring, and restore coordination across supported services. Backup plans define frequency, backup windows, vault destinations, lifecycle rules, and copy actions.
The wider service mix still matters:
- Amazon S3 Versioning and Object Lock protect object histories and retention-sensitive records.
- Amazon RDS and Amazon Aurora support automated backups, snapshots, and point-in-time recovery.
- Amazon EBS snapshots protect block storage and can support application-consistent workflows.
- AWS Elastic Disaster Recovery supports low-RPO replication for selected server recovery cases.
- Native service controls may complement centralized cloud backup solutions AWS teams manage through one governance model.
Do not assume centralized scheduling removes service-specific design. Database consistency, application quiescing, encryption behaviour, restore permissions, and feature availability still differ by resource type and region.
How to Set Backup Policies and Retention Rules
Retention should begin with a reason, not a round number. “Keep monthly copies for seven years” may be valid for a regulated record. It may be wasteful for a system whose source transactions already live in an immutable archive.
Useful data retention strategies AWS teams can apply include short operational recovery, medium-term investigation, long-term recordkeeping, and isolated cyber recovery. Each tier should define frequency, retention, destination account, destination region, vault controls, and test cadence.
AWS Backup lifecycle rules can move eligible recovery points from warm storage to cold storage and later delete them. Cold storage carries a minimum 90-day storage duration. AWS recommends keeping an initial warm full backup long enough to avoid unnecessary replacement full backups.
A policy should also answer three deletion questions:
- Who can shorten retention?
- Who can delete the vault or its encryption key?
- What survives if the production account is compromised?
Cross-account copies reduce shared administrative exposure. Cross-Region copies address regional loss. AWS Backup Vault Lock can enforce retention in governance or compliance mode. After the grace period, a compliance-mode lock cannot be altered or removed while protected recovery points remain.
Logically air-gapped vaults add locked isolation and controlled sharing for recovery from another account. They can also serve as primary destinations for supported backups, reducing the need to retain an additional standard-vault copy solely for isolation.
Turning Backup Compliance into Evidence
Backup compliance AWS programs often fail during audit preparation because policy documents and operational records live apart. A written control may require daily copies, yet no one can show whether all tagged resources were protected, copy jobs succeeded, or retention was changed.
AWS Backup Audit Manager evaluates controls such as backup frequency, minimum retention, encryption, cross-account copy, cross-region copy, and Vault Lock. It can produce daily and on-demand reports for governance evidence.
Evidence should include failed jobs, excluded resources, policy changes, restore tests, recovery duration, and unresolved exceptions. This makes data protection measurable. It also exposes quiet gaps, such as newly deployed assets missing the expected tags or protected resources whose restoration permissions have expired.
Compliance reporting must show more than policy presence. It should prove that the assigned controls operated throughout the reporting period. A resource protected today does not erase a missed backup from last month. Retain activity reports and exception records for the same period covered by the underlying obligation.
How to Reduce Cloud Backup Cost Without Weakening Recovery
Cost reduction should remove redundant retention, avoidable full copies, and low-value duplication. It should not remove the only copy that survives a likely failure.
Use these checks:
- Match backup frequency to the approved RPO.
- Move eligible long-retention recovery points to cold storage at the right time.
- Delete copies when their business or regulatory purpose ends.
- Separate production retention from lower-environment retention.
- Track copy, storage, restore, and cross-region transfer costs by application.
- Test representative recoveries before expanding cloud backup coverage.
Restore testing is the strongest optimization tool because it identifies unusable copies, excessive recovery steps, missing permissions, and unrealistic RTO assumptions, making AWS Well-Architected Reviews useful for finding resilience and recovery gaps. A smaller set of tested recovery points offers more operational value than a large collection no team has restored.
Review backup cost together with recovery time. Moving older copies into cheaper storage may reduce monthly spend while increasing retrieval time. That trade-off is acceptable only when the relevant workload tier can absorb the delay.
Build the Strategy Around Proof
An enterprise backup strategy should be judged by recoverability, isolation, policy coverage, and evidence. Service configuration is only one layer. Ownership, dependency mapping, immutable retention, cross-account design, and repeated restoration determine whether the plan holds during an incident.
Strong AWS data protection also accepts that workloads differ. Apply tighter objectives where interruption threatens revenue, safety, or contractual commitments. Use simpler controls where systems can be recreated.
The final measure is direct: when primary systems fail, can the organization recover clean data and return the service within the time the business approved? That answer determines whether cloud backup is an operational safeguard or merely another storage expense.
Author

Yogita Jain
Content Lead
Yogita Jain leads with storytelling and Insightful content that connects with the audiences. She’s the voice behind the brand’s digital presence, translating complex tech like cloud modernization and enterprise AI into narratives that spark interest and drive action. With a diverse of experience across IT and digital transformation, Yogita blends strategic thinking with editorial craft, shaping content that’s sharp, relevant, and grounded in real business outcomes. At Cygnet, she’s not just building content pipelines; she’s building conversations that matter to clients, partners, and decision-makers alike.