
A permission can outlive the business decision that justified it. An analyst moves to procurement, keeps an old finance reporting role, receives purchasing access, and continues working without any obvious problem. The identity remains valid across both systems. The excess authority stays largely invisible until someone compares the employee’s current responsibilities with the permissions still available.
That is the difficulty behind IT access reviews. Access accumulates through daily work, while removal depends on separate owners and systems. A completed onboarding ticket says little about what happened after a transfer. A signed review says even less if the approved removals never reached the application.
The 2026 Verizon Data Breach Investigations Report identifies credential abuse as an initial access vector in 13% of breaches. This does not measure excess permissions, but compromised accounts can do more damage when their authority has accumulated. Permission drift management therefore belongs in routine IT operations, where managed IT services can help keep access reviews, removals, exceptions, and evidence connected.
Why Permission Drift Builds Across Enterprise Systems
Permissions often expand through individually reasonable requests that produce an unreasonable result. Temporary project access stays open after delivery. A manager approves a new role without identifying the old groups that should disappear. A supplier retains a portal account because the contract ends before anyone tells IT.
The problem deepens when applications enforce rights differently. A directory group may provide sign-in, an application role may permit exports, and a local administrator setting may allow configuration changes. Removing one assignment may leave the others intact. Even a well-maintained identity platform cannot confirm access held directly inside a disconnected application without additional records or integration.
For permission drift management, the most useful question is specific: Which entitlement no longer has a current business reason? A list of inactive users cannot answer it. An employee may use a system daily while retaining a sensitive, unrelated function.
IT access reviews need a dependable inventory of identities, systems, entitlements, and accountable owners, making IT infrastructure management important for connecting access records with actual systems. The inventory must distinguish inherited group rights from direct grants, standing privileges from temporary access, and employee accounts from supplier and service identities. Otherwise, reviewers may miss rights excluded from the review.
Joiner-Mover-Leaver Workflows Need Different Removal Rules
Joiners attract attention because employees cannot work without access. Movers create a quieter problem: transitions appear successful even when old rights remain. Leavers create a more immediate deadline, especially where access exists outside central sign-in controls.
A sound user access review process treats each event as a change in authority, with an expected result that can be verified.
| Workforce event | Common access gap | Operational check |
| Joiner | Broad template grants or unrecorded exceptions | Match assignments to the approved role and expiry conditions |
| Mover | Previous department rights remain after new grants | Compare former and current roles, then remove obsolete entitlements |
| Leaver | Local, vendor, or privileged accounts remain active | Confirm disabling, token revocation, and application-level removal where applicable |
| Contractor extension or exit | Expiry dates no longer match the engagement | Revalidate sponsor, purpose, and end date |
For movers, HR data should trigger a comparison rather than another provisioning task. The outgoing business owner identifies what can end; the incoming owner approves what is newly required. Where work must overlap, an exception should have a named sponsor and an expiry date. Without those details, a temporary overlap becomes permanent by default.
Leaver handling also needs separate attention for active sessions, locally managed credentials, personal access tokens, and shared secrets known to the departing person. Disabling a directory account may interrupt centralized sign-in while leaving some existing sessions or application-specific access unaffected. The result depends on each system’s authentication method.
Good identity governance operations connect these lifecycle events to tickets, approvals, technical changes, and closure evidence. If a downstream system fails to process a removal, the failure must remain visible as unfinished work. A workflow marked complete while an account remains active is a control failure.
What IT Access Reviews Should Actually Test
A campaign can collect hundreds of approvals and still produce weak decisions. A manager sees unfamiliar entitlement names, has limited context, and selects retain because removing access might interrupt work. Repeating that exercise quarterly creates records, but little assurance.
Useful IT access reviews provide the reviewer with the business function, last relevant activity where available, grant source, sensitivity of the role, and reason for the original assignment. They also identify who is authorized to decide. A line manager may know the employee’s duties, while the application owner understands the effect of an administrator permission. Both perspectives matter for sensitive entitlements.
The user access review process needs actionable decisions: retain with a reason, remove, reduce the privilege, or grant a documented time-bound exception. Unanswered items should follow a defined escalation policy. Automatically treating silence as approval conceals weak ownership; automatically removing everything can disrupt services. Policy must reflect resource risk and recovery options.
Access recertification is particularly vulnerable to blanket approval. A better review separates ordinary roles from privileged and exceptional grants, then asks reviewers to assess the outliers first. Recent use can inform that decision, but inactivity alone is weak evidence. Emergency access may be legitimate despite infrequent use, while an overprivileged user could be active every day.
Another check deserves attention: coverage. How many applications, local roles, privileged accounts, and external identities were actually included? A flawless approval rate means little when high-risk systems are absent. For permission drift management, missing entitlements can be more important than late reviewer responses.
Privilege Cleanup Must Reach the Source of Access
Removing an employee from a group might leave the effective right intact. Another group could grant the same permission, a direct assignment might remain, or an application could maintain its own local role. The distinction matters most for administrative access, bulk data exports, production changes, and financial approvals.
Least privilege enforcement starts with understanding the permission path. Teams should trace each right’s origin, inheritance, and alternate grant paths. That assessment can reveal persistent administrator assignments disguised by otherwise ordinary job profiles.
Practical cleanup involves more than deleting accounts:
- Replace standing elevated rights with time-limited elevation where the platform supports it.
- Retire unused direct grants after checking for inherited or alternate permissions.
- Review emergency accounts and service identities under separate ownership and usage rules.
- Reconcile revoked entitlements against the application’s effective access state.
These checks support permission drift management without treating every exception as an incident. Some exceptions are necessary for continuity. The difference is whether the exception has an owner, defined purpose, expiry or review condition, and evidence of approval.
Endpoint controls cannot substitute for managing what authenticated identities can do. Cybersecurity services should therefore include privilege inventories, change monitoring, and validation after removal, alongside the organization’s existing authentication safeguards.
Audit Evidence Should Prove That Access Changed
An access review report frequently shows the reviewer, decision, and completion date. Auditors may also need to establish whether the resulting change occurred and whether the control operated within policy. An approved removal that sits in a service queue is still open exposure.
Evidence should link the identity, entitlement, reviewer, decision, execution record, and verification result. If removal failed, the record should show the reason, current owner, escalation, and eventual resolution. Evidence should come from the system where the permission is enforced whenever that is feasible.
NIST SP 800-53’s account management control addresses account reviews and alignment with personnel transfers and terminations. Its least privilege guidance also supports periodic examination of assigned rights. Neither makes a signed spreadsheet equivalent to confirmed revocation.
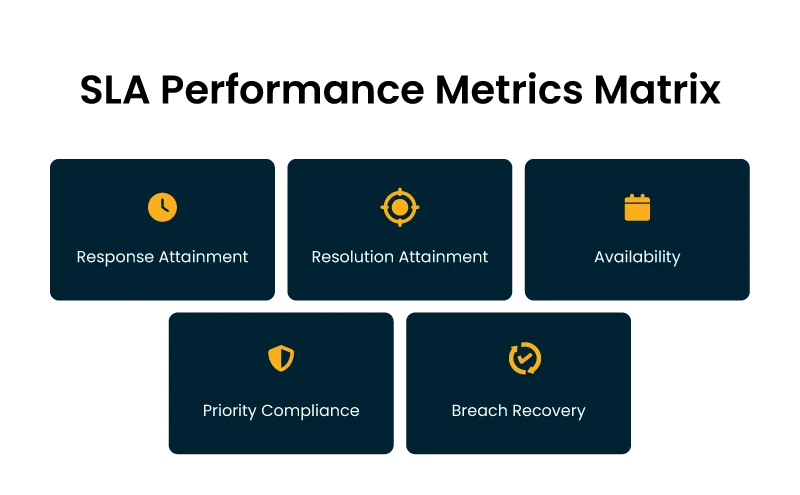
Here, access recertification becomes an operations question. The useful measure is the decision-to-removal gap: how long an unnecessary entitlement remains effective after its removal is approved. A separate event-to-revocation gap shows the delay after a role change or departure. Both expose handoffs that a campaign completion percentage can hide.
For identity governance operations, audit preparation becomes easier when these records are collected as part of everyday work. Reconstructing decisions months later can miss exceptions handled outside the usual workflow.
How Managed IT Creates a Reliable Access Review Cadence
Permission drift management needs repeatable follow-through across systems with different owners and administrative methods. Security defines policy and risk tolerance. Business owners decide legitimate need. Managed IT runs the schedule, reconciles identities, routes decisions, performs authorized changes, and confirms closure as part of broader IT strategy and consulting. Keep those boundaries explicit.
A workable cadence combines several triggers rather than relying on a single review month:
- On each lifecycle event: Process joiners, movers, leavers, and contract expiries against defined completion conditions.
- During routine operations: Identify failed removals, orphaned accounts, expiring exceptions, and unexpected privileged grants.
- At risk-based intervals: Run IT access reviews for sensitive applications, administrator roles, vendor accounts, and other agreed resources.
- During service reviews: Examine overdue decisions, unresolved exceptions, missing system coverage, and changes to access ownership.
Managed IT security controls must include applications outside centralized identity tooling. An export from an application administrator may be necessary, followed by owner review, manually approved removal, and a fresh export confirming the result. Manual checks are preferable to false coverage.
Least privilege enforcement improves when a managed team records repeat exceptions and investigates the underlying design. If employees repeatedly request the same broad group to perform a narrow task, the group may need redesign. If departures routinely leave local accounts behind, the application needs an explicit offboarding step. Repeated findings should change procedures rather than create more cleanup tickets.
Successful permission drift management depends on this feedback. The reporting question shifts from how many reviews finished to which rights were removed, which remain under approved exception, and which systems have yet to provide reliable evidence. That makes a managed service review useful to both IT leadership and business owners.
Close the Gap Between Access Decisions and Actual Permissions
Permissions remain clean when the organization can explain each material grant, detect when the reason changes, and prove that unnecessary authority was removed. Those are ongoing responsibilities across HR, application owners, security, and IT operations.
IT access reviews provide the decision point, but operational discipline determines the result. A review that identifies obsolete access without closing the removal task has exposed a weakness rather than resolved it. Stronger permission drift management ties lifecycle events, reviewer decisions, technical execution, and evidence into the same accountable workflow.
Start with a sensitive application: trace a recent role change through entitlement removal, then inspect the final access state. The missing handoff in that journey is a better starting point than another organization-wide approval campaign.
Author

Yogita Jain
Content Lead
Yogita Jain leads with storytelling and Insightful content that connects with the audiences. She’s the voice behind the brand’s digital presence, translating complex tech like cloud modernization and enterprise AI into narratives that spark interest and drive action. With a diverse of experience across IT and digital transformation, Yogita blends strategic thinking with editorial craft, shaping content that’s sharp, relevant, and grounded in real business outcomes. At Cygnet, she’s not just building content pipelines; she’s building conversations that matter to clients, partners, and decision-makers alike.